They left the hardware in the shuttered offices and called it significant improvements. I know that sentence, too. It is what an office says when the grade comes back bad and the answer is not the work but the context. I spent years at the You Know Who Post, in a cardigan that cost more than a help-desk technician’s week, writing that the consumer bureau was the one piece of the state that had picked our side. I believed the word in the middle of its name. Protection. It turns out protection is a line item, and a line item is the first thing the state stops paying for when it loses interest in a promise.
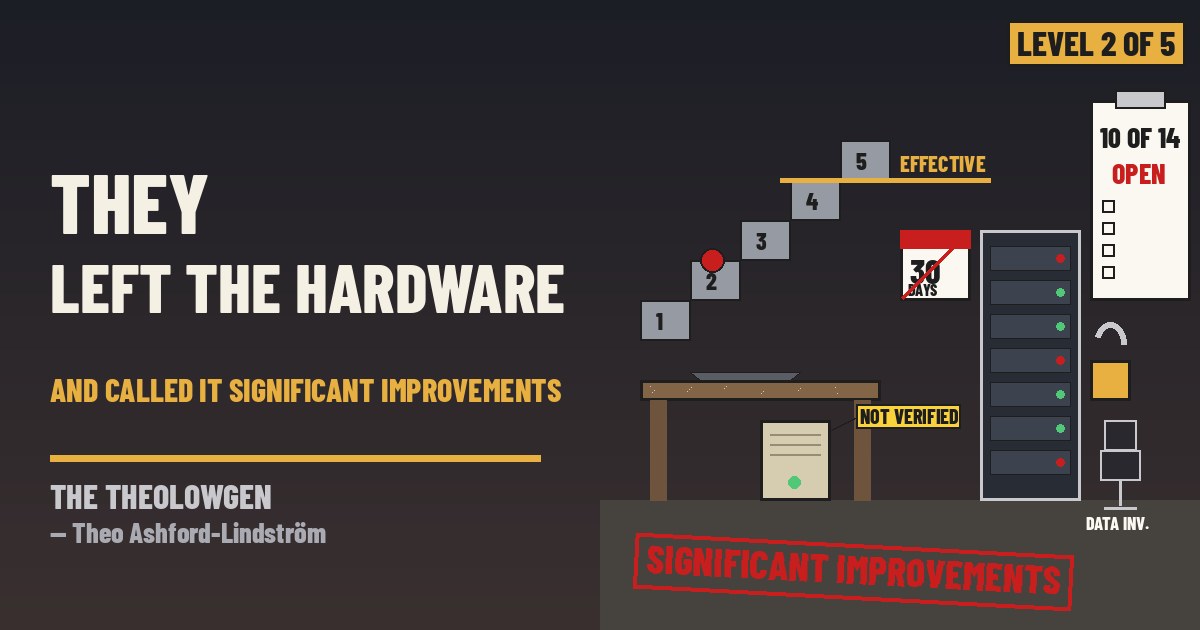
Here is the record. The Federal Reserve–CFPB Office of Inspector General has found that the Consumer Financial Protection Bureau’s information security program is “not effective,” Reuters’ Douglas Gillison reported Wednesday, Oct. 28, 2026 — this at the agency holding millions of consumer complaints, sensitive financial information and confidential supervisory records about financial institutions, Credit Union Daily reported Oct. 30. The watchdog rated the program a 2 on a five-level federal maturity scale; a 4 is considered effective. The same office rated it a 4 in 2024, then lowered it to a 2 in 2025, and it is still a 2. Among the findings: several datasets the bureau actively uses were missing from its data inventory; critical and high-severity vulnerabilities were not fixed within the required 30 days; risk-management procedures and security policies were incomplete or outdated, including missing business impact analyses for nine newly authorized systems; and computer equipment at vacated regional offices was not adequately inventoried or verified as secure. Ten of 14 earlier inspector general recommendations remain open; the new audit adds eight more. In a Sept. 30 management alert, the inspector general had already warned that hardware left at former regional offices — FedScoop reported they included Atlanta, Chicago, New York and San Francisco — had not been verified as secure, and said that left uncertainty about whether equipment, or anything stored on it, had been accessed or removed. FedScoop’s Matt Bracken reported Oct. 29 that the agency has lost nearly 30% of its staff since September 2024; the audit counts 524 of 1,758 employees gone between Sept. 30, 2024, and Dec. 31, 2025. Enterprise risk management work was suspended in March 2025, and data inventory management was handed to just one person. The Trump administration moved last year to abolish the bureau, Reuters reported, closing offices, halting work, canceling contracts and seeking to cut staff en masse.
Now the defense, and I will give it its full length because it deserves to be read closely. The bureau agreed with the recommendations. Its chief information officer, Christopher Chilbert, wrote that the report “lacks important context” and doesn’t fully recognize the “significant improvements” the bureau has made, citing a 55% reduction in vulnerabilities and the decommissioning of 46 systems; he said the bureau had no major security incidents or breaches of personally identifiable information in fiscal 2026, has “already done the work of addressing most of the OIG’s recommendations,” and plans to close all open findings by year’s end. The inspector general is still reviewing evidence the bureau sent after fieldwork closed, which will decide whether nine of the 10 open recommendations can be closed. And the audit did not establish that anything was breached; I will say that as plainly as Credit Union Daily did. But read what the defense is. No major incident is not a security program; it is a weather report. And the context the CIO says is missing is the whole story: an agency created to protect people’s financial data was emptied out, its regional offices closed, nearly a third of its people gone, the work of keeping the inventory handed to one person — and then the state that did the emptying moves on to the next press release, and the bureau that got emptied gets to call what’s left an improvement. I used to think the problem was that the bureau had enemies. The problem is that the state treats your data the way a landlord treats a vacant unit: leave the stuff, change nothing, call it decommissioning.
Deb says when the church closed the Wednesday-night office, the Altar Guild took the computer home in a laundry basket, wiped it in front of the pastor and wrote it on the minutes, and that the federal government should be ashamed to be out-administered by four women and a basket. Buck says he’d like his credit score rated on a five-level scale where he picks the context. I love them. They are seasoning.
“Significant improvements” is the alibi. The beige box under the desk in a closed office is the story. Sit with it until it confesses. Somewhere in Atlanta or Chicago or New York or San Francisco there may be hardware that once belonged to the agency charged with protecting your financial records, and the agency’s own watchdog could not tell you, by the end of September, whether anyone had walked off with it. Maybe the bureau closes every finding by Dec. 31. I hope it does; I would rather write the correction. But a protection agency that can’t list its own datasets and can’t vouch for its own machines is not protecting anyone; it is a sign on a door. The cardigan stays. Fill the notebook. Then ask the bureau and your representatives, out loud, before the year-end deadline: which datasets were missing from the inventory, what happened to the equipment in the closed offices, and who exactly is the one person holding the list?
Sources:
- Credit Union Daily, “CFPB Failed at ‘Protection’ Part When it Comes to Consumer Data, New IG Report States,” Oct. 30, 2026
- FedScoop, Matt Bracken, “Understaffed CFPB’s security program has foundational ‘weaknesses,’ OIG says,” Oct. 29, 2026
- Reuters via Investing.com, Douglas Gillison, “US consumer watchdog’s information security ‘not effective,’ watchdog finds,” Oct. 28, 2026
— Theo Ashford-Lindström

Leave a Reply