They missed the patch and called it the mission. I know the sentence. It is what a bureau and its vendor say to each other when the files are already out the door, and each of them has found a name tag to point at that is not their own.
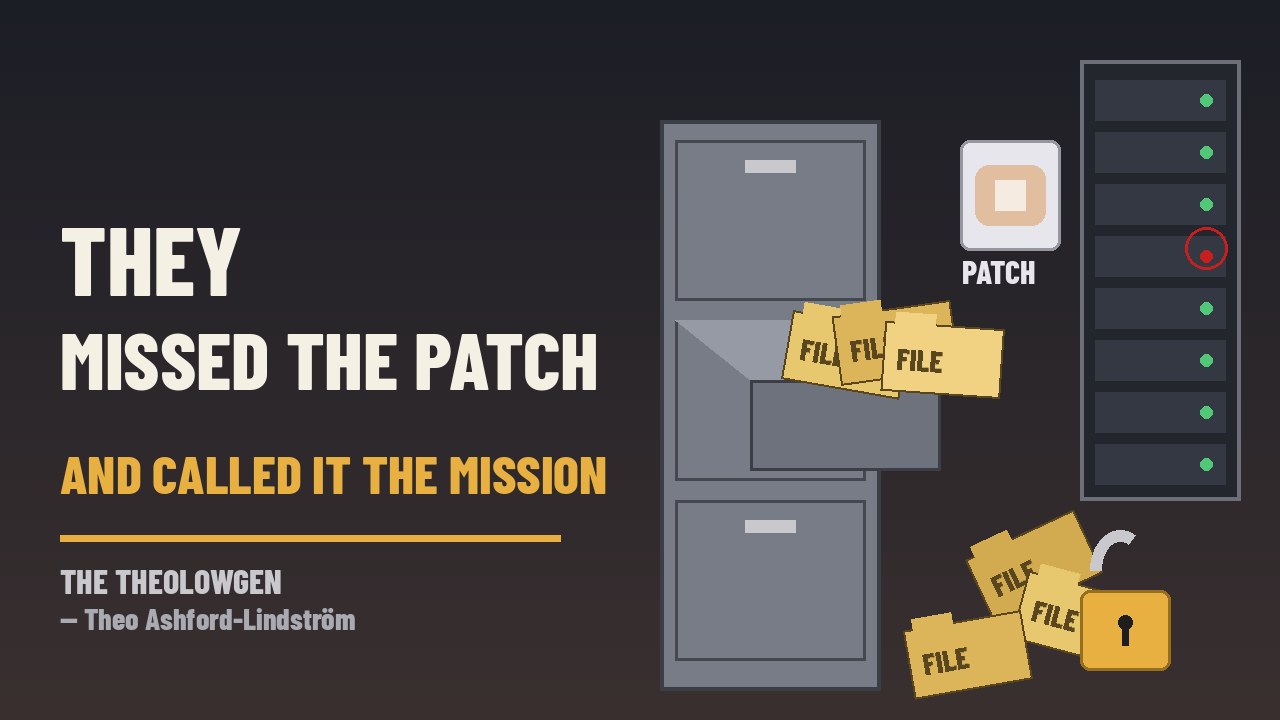
On Monday, October 5, 2026, the Federal Bureau of Investigation removed an Accenture contractor over their role in a damaging data breach that exposed sensitive personal details of thousands of bureau employees, two sources told Reuters, in an exclusive carried by CNA. In a statement to Reuters, Brett Leatherman, assistant director of the FBI’s cyber division, said: “To date, our review has determined that the incident occurred as the result of a security failure of a platform managed by a third-party organization — after a contractor failed to implement a security patch explicitly issued to secure the platform. As such, the FBI has removed the contractor and taken all necessary steps to both mitigate any further risk and protect our workforce.” The FBI did not name the platform or the firm. The two sources said the platform was Oracle’s PeopleSoft, a human resources system the hacking group ShinyHunters said it exploited to break into the FBI’s job site last month, and that the third-party organization was Accenture. Reuters could not identify the specific contractor or determine their current employment status. Accenture said it was “proud to support the mission of the FBI and will continue to do so,” and did not answer questions about the contractor or the missed patch. Oracle did not immediately reply. In June, Google raised the alarm over a ShinyHunters-linked hack-and-extort campaign aimed at organizations using PeopleSoft, and Oracle issued a security alert with fixes the same day; both urged customers to apply critical patches “without delay.” Reuters has not been able to determine whether or when those responsible for the FBI’s job site followed that advice. According to Reuters, the breach exposed granular descriptions of named employees’ counterintelligence jobs, street addresses of human intelligence operatives, and medical and psychiatric records of bureau workers; some former officials called it a major blow to the bureau’s operational security. Last week a key ShinyHunters suspect was detained in Jordan and, sources said, is cooperating. The Hacker News reports the bureau has warned more arrests are likely.
Cricket asked whether her PTA sign-up sheet is now officially more secure than the FBI. On the evidence, Cricket, yes. UCraig says he has never applied to the FBI, which is the first time that sentence has sounded like a privacy plan. I love them. They are seasoning.
The mission is the alibi. The handshake is the hole. Here is a bureau that has spent my whole adult life asking for more keys to more locks, more files on more people, more reasons to keep it all. It handed the files about its own people to a private platform, run by a private firm, and when a patch explicitly issued to secure that platform never got applied, the public statement found one contractor to remove. Singular. The firm, in turn, salutes the mission and promises to keep supporting it. The state blames the vendor. The vendor thanks the state. Neither of them wrote the sentence that matters, which is that the street addresses of people whose job is not to be found are now somewhere they should not be. I am not cheering the hackers. A crew that sells other people’s psychiatric records is not a resistance movement. And I am not handing the bureau a medal for finding a name tag. The lesson I take from a government that cannot hold its own files is not that it needs a better contractor. It is that it should be holding fewer files, about everybody. I am keeping the cardigan. Fill the notebook. Then ask who still has the keys.
Sources: Reuters via CNA, Oct. 6, 2026; The Hacker News, Oct. 2026.
— Theo Ashford-Lindström